You can enable database audit only after the agent is installed. This topic describes how to install the agent on a node running a Linux OS.
Prerequisites
- You have added an agent to your database.
- You have obtained the agent installation package for the Linux OS.
- The Linux OS version of the target node is supported by the agent.
Scenarios
You can install the agent on the database or application side, depending on your database type and deployment scenario. Common database scenarios are as follows:
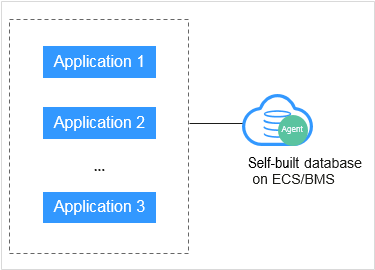
- Deploy DBSS for databases built on ECS/BMS. For details, see Figure 1 and Figure 2.
Figure 1 One application connecting to multiple databases built on ECS/BMS
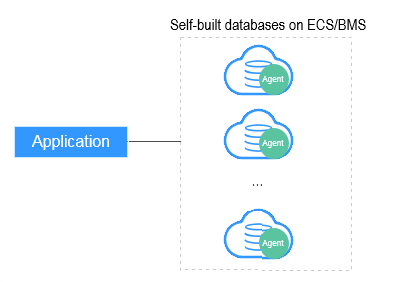
Figure 2 Multiple applications connecting to one database built on ECS/BMS
- Deploy DBSS for RDS databases. For details, see Figure 3 and Figure 4.
Figure 3 One application connecting to multiple RDS databases
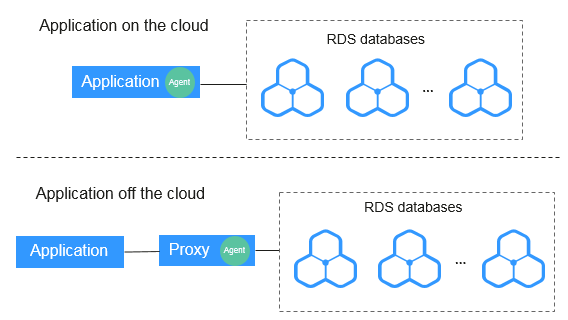
Figure 4 Multiple applications connecting to one RDS database
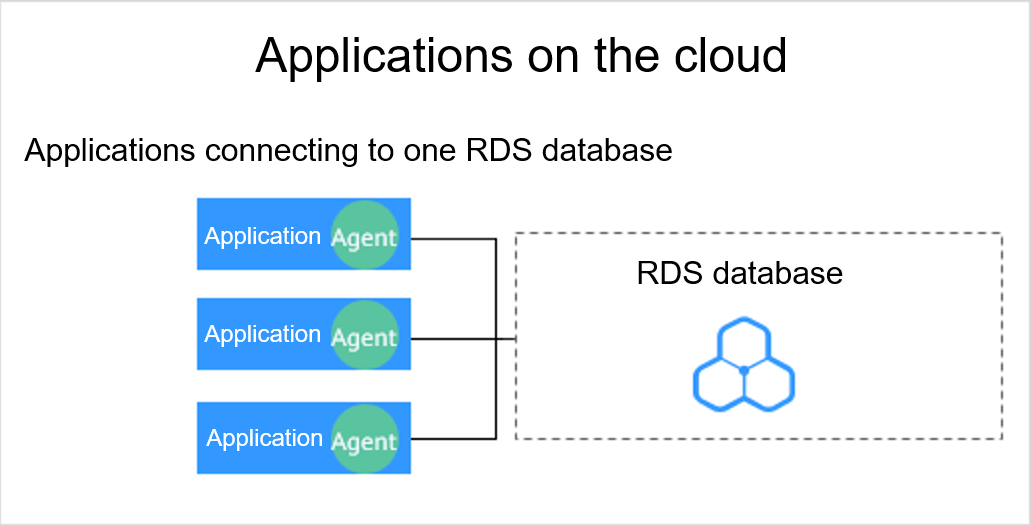
Table 1 describes where to install the agent in the preceding scenarios.
If your applications and databases (databases built on ECS/BMS) are deployed on the same node, install the agent on the database side.
Scenario | Where to Install Agent | Audit Scope | Description |
|---|---|---|---|
Self-built database on ECS/BMS | Database | All access records of applications that have accessed the database |
|
RDS database | Application side (if applications are deployed on the cloud) | Access records of all the databases connected to the application |
|
RDS database | Proxy side (if applications are deployed off the cloud) | Only the access records between the proxy and database. Those between the applications and database cannot be audited. | Install the agent on the proxy side. |
Installing an Agent
When installing a new agent, you need to customize a password for it.
Install the agent on the node suitable for your service scenario.
- Upload the downloaded agent installation package xxx.tar.gz to the node (for example, using WinSCP).
- Log in to the node as user root using SSH through a cross-platform remote access tool (for example, PuTTY).
- Run the following command to access the directory where the agent installation package xxx.tar.gz is stored:
cd Directory_containing_agent_installation_package
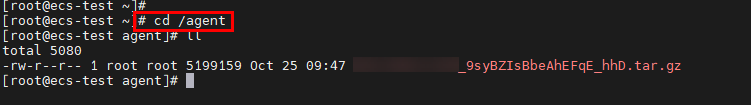
- Run the following command to decompress the installation package xxx.tar.gz:
tar -xvf xxx.tar.gz

- Run the following command to switch to the directory containing the decompressed files:
cd Decompressed_package_directory
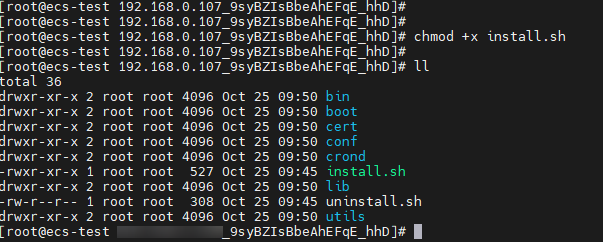
- Run the following command to check whether you have the permission for executing the install.sh script:
ll
- If you do, go to 7.
- If you do not, perform the following operations:
- Run the following command to get the script execution permission:
chmod +x install.sh
- Verify you have the required permissions.
- Run the following command to get the script execution permission:
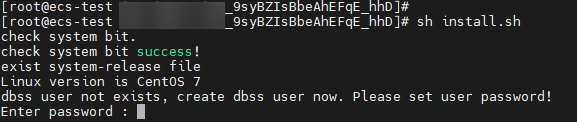
- Run the following command to install the agent:
sh install.sh
 Note
- In Ubantu, run the bash install.sh command to install the agent.
- The agent program is run by common DBSS users. When installing the agent for the first time, you need to create an agent user. After running the sh install.sh command, you need to set a password for the DBSS user.
If the following information is displayed, the agent has been installed. Otherwise, the installation fails.
12345start agentstarting audit agentaudit agent startedstart successinstall dbss audit agent done!NoticeIf the agent installation failed, ensure the OS version of the target node is supported and try again.
- Run the following command to view the running status of the agent program:
service audit_agent status
If the following information is displayed, the agent is running properly:
 audit agent is running.