Network policies are designed by Kubernetes to restrict pod access. Like a firewall at the application layer, network policies enhance network security. The capabilities supported by network policies depend on the capabilities of the network add-ons of the cluster.
By default, if a namespace does not have any policy, pods in the namespace accept traffic from any source and send traffic to any destination.
The following selectors are available for network policies:
- namespaceSelector: selects particular namespaces for which all pods should be allowed as ingress sources or egress destinations.
- podSelector: selects particular pods in the same namespace as the network policy which should be allowed as ingress sources or egress destinations.
- ipBlock: selects particular CIDR blocks to allow as ingress sources or egress destinations.Note
In addition to service ports and CIDR blocks, you must account for ports and CIDR blocks required by critical cluster components such as CoreDNS and NodeLocal DNSCache. Omitting these may affect service stability.
Relationships Between Network Policies and Cluster Types
Cluster Type | CCE Standard Cluster | CCE Standard Cluster | CCE Turbo Cluster |
|---|---|---|---|
Network Model | Tunnel Network | VPC Network | Cloud Native Network 2.0 |
Network policies | Enabled by default | Disabled by default (To use network policies, enable DataPlane V2 when creating a cluster.) | Disabled by default (To use network policies, enable DataPlane V2 when creating a cluster.) |
Data plane implementation | OpenvSwitch | eBPF | eBPF |
Cluster versions for ingress rules | All versions | v1.27.16-r30, v1.28.15-r20, v1.29.13-r0, v1.30.10-r0, v1.31.6-r0, or later | Clusters v1.34.3-r10 or later |
Cluster versions for egress rules | v1.23 and later | ||
Selector for ingress rules | namespaceSelector podSelector | namespaceSelector podSelector ipBlock | namespaceSelector podSelector ipBlock |
Selector for egress rules | namespaceSelector podSelector ipBlock | ||
Maximum number of NetworkPolicy objects that can be applied to a pod | 15 | Not limited. It is recommended to keep the number below 100. | Not limited. It is recommended to keep the number below 100. |
Supported OS | EulerOS CentOS HCE OS 2.0 | HCE OS 2.0 is supported. Clusters v1.28.15-r70, v1.29.15-r30, v1.30.14-r30, v1.31.10-r30, v1.32.6-r30, v1.33.5-r20, v1.34.1-r0, and later versions support Ubuntu 22.04. | HCE OS 2.0 is supported. Clusters v1.28.15-r70, v1.29.15-r30, v1.30.14-r30, v1.31.10-r30, v1.32.6-r30, v1.33.5-r20, v1.34.1-r0, and later versions support Ubuntu 22.04. |
IPv6 network policies | Not supported | Not supported | Supported |
Secure containers | Not supported | Not supported | Not supported |
IPBlock scope | No limitations | Subnets within the pod CIDR block, Service CIDR block, and node IP addresses | Subnets within the pod CIDR block, Service CIDR block, and node IP addresses |
Limiting ClusterIP access through workload labels | Not supported | Supported | Supported |
Limiting the internal cloud server CIDR block of 100.125.0.0/16 | Supported | Supported | Supported |
SCTP | Not supported | Supported | Supported |
Always allowing access to pods on a node from other nodes | Supported | Supported | Supported |
Configuring EndPort in network policies | Not supported | Supported | Supported |
- If you upgrade a CCE standard cluster with a tunnel network to a version that supports egress rules in in-place mode, the rules will not work because the node OS is not upgraded. In this case, reset the node.
- When a network policy is enabled for a cluster with a tunnel network, a pod's source IP address is embedded in the optional field of packets it sends to any Service CIDR block. This enables the configuration of network policy rules on the destination pod, taking into account the source IP address of the pod.
Using Ingress Rules
Scenario 1: Allowing Only Pods with Specified Labels to Access the Target Pod
Figure 1 podSelector
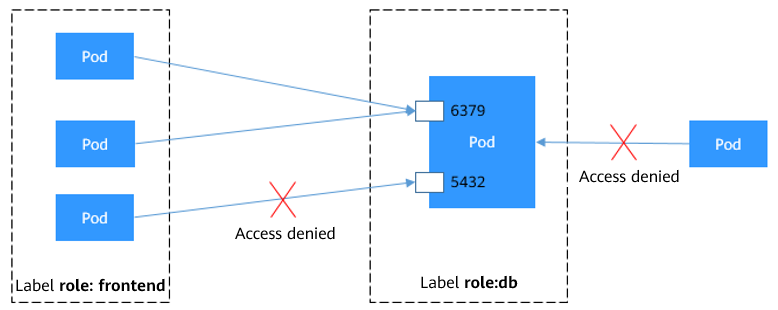
For example, a pod labeled role=db exposes port 6379 and accepts traffic only from pods labeled role=frontend. To achieve this, take the following steps:
Using the CCE Console
- Log in to the CCE console and click the cluster name to access the cluster console.
- Choose Policies in the navigation pane, click the Network Policies tab, and click Create Network Policy in the upper right corner.
- Configure network policy parameters.
Table 1 Parameters for creating a network policy Parameter
Description
Example
Policy Name
Customize the name for the network policy.
access-ingress1
Namespace
Select the namespace where the policy applies.
default
Selector
Enter a label selector for the target pod and click Add. If left empty, all pods in the namespace are selected. Click Reference Workload Label to use an existing workload's label.
Key: role
Value: db
Inbound Rule
Click
 to add an inbound rule.
Outbound Rule
Click
 to add an outbound rule.
N/A
Table 2 Parameters for adding an inbound rule Parameter
Description
Example
Protocol & Port
Select the protocol type and port. TCP and UDP are supported.
Protocol: TCP
Port: 6379
Source CIDR Block
For clusters v1.27.16-r10, v1.28.15-r0, v1.29.10-r0, v1.30.6-r0, or later versions with DataPlane V2 enabled, you can configure the source CIDR block.
The specified source CIDR block allows traffic from a destination CIDR block (multiple exception CIDR blocks can be specified). Separate the destination and exception CIDR blocks using a vertical bar (|). If there are multiple exception CIDR blocks, separate them using commas (,). For example, 172.17.0.0/16|172.17.1.0/24,172.17.2.0/24 allows traffic from 172.17.0.0/16 except 172.17.1.0/24 and 172.17.2.0/24.
N/A
Source Namespace
Select a namespace whose objects can be accessed. It defaults to the policy's namespace if unspecified.
default
Source Pod Label
Enter a label selector for the allowed source pods and click Add. If left empty, all pods in the source namespace are permitted.
Key: role
Value: frontend
- Click OK.
Using a YAML File
- Create the access-ingress1.yaml file.vim access-ingress1.yaml
File content:
apiVersion: networking.k8s.io/v1kind: NetworkPolicymetadata:name: access-ingress1namespace: defaultspec:podSelector: # This rule applies only to pods labeled role=db .matchLabels:role: dbingress: # This is an ingress rule.- from:- podSelector: # Allow access only from pods labeled role=frontend .matchLabels:role: frontendports: # Only TCP can be used to access port 6379.- protocol: TCPport: 6379 - Run the following command to create the network policy defined in the access-ingress1.yaml file:kubectl apply -f access-ingress1.yaml
Expected output:
networkpolicy.networking.k8s.io/access-ingress1 created
Scenario 2: Allowing Only Pods in a Specific Namespace to Access the Target Pod
Figure 2 namespaceSelector
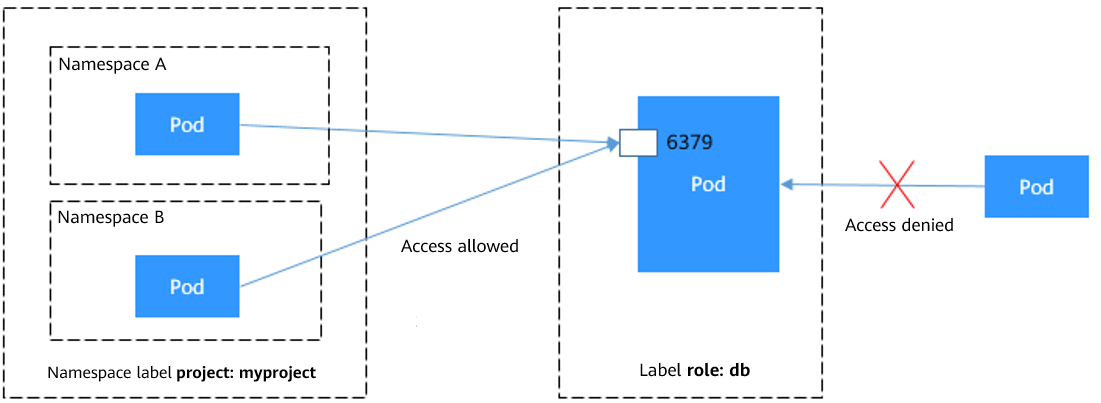
The pod labeled role=db only permits access to its port 6379 from pods in the namespace labeled project=myproject. To achieve this, take the following steps:
Using the CCE Console
- Log in to the CCE console and click the cluster name to access the cluster console.
- Choose Policies in the navigation pane, click the Network Policies tab, and click Create Network Policy in the upper right corner.
- Configure network policy parameters.
Table 3 Parameters for creating a network policy Parameter
Description
Example
Policy Name
Customize the name for the network policy.
access-ingress2
Namespace
Select the namespace where the policy applies.
default
Selector
Enter a label selector for the target pod and click Add. If left empty, all pods in the namespace are selected. Click Reference Workload Label to use an existing workload's label.
Key: role
Value: db
Inbound Rule
Click
 to add an inbound rule.
Outbound Rule
Click
 to add an outbound rule.
N/A
Table 4 Parameters for adding an inbound rule Parameter
Description
Example
Protocol & Port
Select the protocol type and port. TCP and UDP are supported.
Protocol: TCP
Port: 6379
Source CIDR Block
For clusters v1.27.16-r10, v1.28.15-r0, v1.29.10-r0, v1.30.6-r0, or later versions with DataPlane V2 enabled, you can configure the source CIDR block.
The specified source CIDR block allows traffic from a destination CIDR block (multiple exception CIDR blocks can be specified). Separate the destination and exception CIDR blocks using a vertical bar (|). If there are multiple exception CIDR blocks, separate them using commas (,). For example, 172.17.0.0/16|172.17.1.0/24,172.17.2.0/24 allows traffic from 172.17.0.0/16 except 172.17.1.0/24 and 172.17.2.0/24.
N/A
Source Namespace
Select a namespace whose objects can be accessed. It defaults to the policy's namespace if unspecified.
myproject
Source Pod Label
Enter a label selector for the allowed source pods and click Add. If left empty, all pods in the source namespace are permitted.
N/A
- Click OK.
Using a YAML File
- Create the access-ingress2.yaml file.vim access-ingress2.yaml
File content:
apiVersion: networking.k8s.io/v1kind: NetworkPolicymetadata:name: access-ingress2spec:podSelector: # This rule applies only to pods labeled role=db .matchLabels:role: dbingress: # This is an ingress rule.- from:- namespaceSelector: # Allow access only from pods in namespaces labeled project=myproject .matchLabels:project: myprojectports: # Only TCP can be used to access port 6379.- protocol: TCPport: 6379 - Run the following command to create the network policy defined in the access-ingress2.yaml file:kubectl apply -f access-ingress2.yaml
Expected output:
networkpolicy.networking.k8s.io/access-ingress2 created
Scenario 3: Allowing Only Pods with Specific Labels in a Specific Namespace to Access the Target Pod
Figure 3 Using both podSelector and namespaceSelector
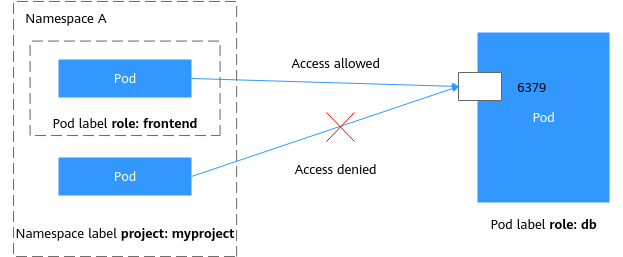
The pod labeled role=db only allows access to its port 6379 from pods with label role=frontend in the namespace labeled project=myproject. To achieve this, take the following steps:
Using the CCE Console
- Log in to the CCE console and click the cluster name to access the cluster console.
- Choose Policies in the navigation pane, click the Network Policies tab, and click Create Network Policy in the upper right corner.
- Configure network policy parameters.
Table 5 Parameters for creating a network policy Parameter
Description
Example
Policy Name
Customize the name for the network policy.
access-ingress3
Namespace
Select the namespace where the policy applies.
default
Selector
Enter a label selector for the target pod and click Add. If left empty, all pods in the namespace are selected. Click Reference Workload Label to use an existing workload's label.
Key: role
Value: db
Inbound Rule
Click
 to add an inbound rule.
Outbound Rule
Click
 to add an outbound rule.
N/A
Table 6 Parameters for adding an inbound rule Parameter
Description
Example
Protocol & Port
Select the protocol type and port. TCP and UDP are supported.
Protocol: TCP
Port: 6379
Source CIDR Block
For clusters v1.27.16-r10, v1.28.15-r0, v1.29.10-r0, v1.30.6-r0, or later versions with DataPlane V2 enabled, you can configure the source CIDR block.
The specified source CIDR block allows traffic from a destination CIDR block (multiple exception CIDR blocks can be specified). Separate the destination and exception CIDR blocks using a vertical bar (|). If there are multiple exception CIDR blocks, separate them using commas (,). For example, 172.17.0.0/16|172.17.1.0/24,172.17.2.0/24 allows traffic from 172.17.0.0/16 except 172.17.1.0/24 and 172.17.2.0/24.
N/A
Source Namespace
Select a namespace whose objects can be accessed. It defaults to the policy's namespace if unspecified.
myproject
Source Pod Label
Enter a label selector for the allowed source pods and click Add. If left empty, all pods in the source namespace are permitted.
Key: role
Value: frontend
- Click OK.
Using a YAML File
- Create the access-ingress3.yaml file.vim access-ingress3.yaml
File content:
apiVersion: networking.k8s.io/v1kind: NetworkPolicymetadata:name: access-ingress3spec:podSelector: # This rule applies only to pods labeled role=db .matchLabels:role: dbingress: # This is an ingress rule.- from:- namespaceSelector: # Allow access only from pods in namespaces labeled project=myproject .matchLabels:project: myprojectpodSelector: # Allow access only from pods labeled role=frontend .matchLabels:role: frontendports: # Only TCP can be used to access port 6379.- protocol: TCPport: 6379 - Run the following command to create the network policy defined in the access-ingress3.yaml file:kubectl apply -f access-ingress3.yaml
Expected output:
networkpolicy.networking.k8s.io/access-ingress3 created
Using Egress Rules
Scenario 1: Restricting Pods to Access Only Specified Addresses
Figure 4 ipBlock
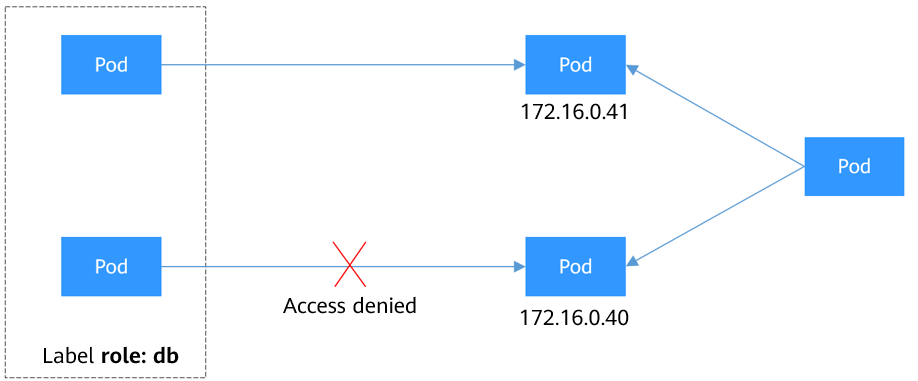
The pods labeled role=db only allow access to 172.16.0.0/16, excluding 172.16.0.40/32. To achieve this, take the following steps:
Using the CCE Console
- Log in to the CCE console and click the cluster name to access the cluster console.
- Choose Policies in the navigation pane, click the Network Policies tab, and click Create Network Policy in the upper right corner.
- Configure network policy parameters.
Table 7 Parameters for creating a network policy Parameter
Description
Example
Policy Name
Customize the name for the network policy.
access-ingress3
Namespace
Select the namespace where the policy applies.
default
Selector
Enter a label selector for the target pod and click Add. If left empty, all pods in the namespace are selected. Click Reference Workload Label to use an existing workload's label.
Key: role
Value: db
Inbound Rule
Click
 to add an inbound rule.
N/A
Outbound Rule
Click
 to add an outbound rule.
Table 8 Parameters for adding an outbound rule Parameter
Description
Example
Protocol & Port
Select the protocol type and port. TCP and UDP are supported. If unspecified, all protocols and ports are permitted.
N/A
Destination CIDR Block
Allow requests to be routed to a specified CIDR block (and not to the exception CIDR blocks). Separate the destination and exception CIDR blocks using a vertical bar (|). If there are multiple exception CIDR blocks, separate them using commas (,). For example, 172.17.0.0/16|172.17.1.0/24,172.17.2.0/24 allows 172.17.0.0/16 except 172.17.1.0/24 and 172.17.2.0/24.
172.16.0.0/16|172.16.0.40/32
Destination Namespace
Select a namespace whose objects can be accessed. It defaults to the policy's namespace if unspecified.
N/A
Destination Pod Label
Label selector for the target pod permitted by this rule. If left empty, all pods in the destination namespace are allowed.
N/A
- Click OK.
Using a YAML File
- Create the access-egress1.yaml file.vim access-egress1.yaml
File content:
apiVersion: networking.k8s.io/v1kind: NetworkPolicymetadata:name: access-egress1namespace: defaultspec:policyTypes: # Must be specified for egress rules.- EgresspodSelector: # This rule applies only to pods labeled role=db .matchLabels:role: dbegress: # This is an egress rule.- to:- ipBlock:cidr: 172.16.0.0/16 # Allows outbound traffic to this CIDR block.except:- 172.16.0.40/32 # Blocks access to this CIDR block, which is in the range specified by the cidr parameter. - Run the following command to create the network policy defined in the access-egress1.yaml file:kubectl apply -f access-egress1.yaml
Expected output:
networkpolicy.networking.k8s.io/access-egress1 created
Scenario 2: Restricting a Pod to Be Accessed Only by Pods with Specified Labels
Figure 5 Using both ingress and egress
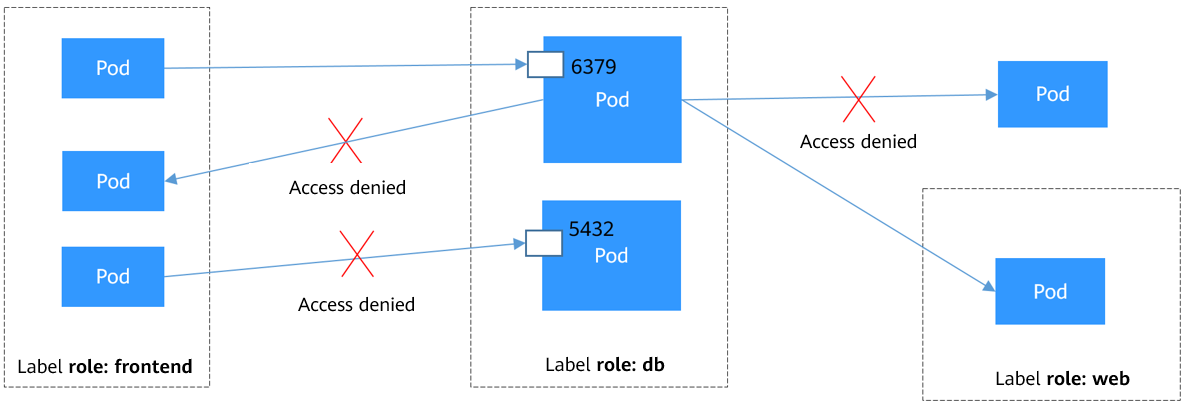
The pod labeled role=db only permits access to its port 6379 from pods labeled role=frontend, and this pod can only access the pods labeled role=web. You can use the same rule to configure both ingress and egress in a network policy. To achieve this, take the following steps:
Using the CCE Console
- Log in to the CCE console and click the cluster name to access the cluster console.
- Choose Policies in the navigation pane, click the Network Policies tab, and click Create Network Policy in the upper right corner.
- Configure network policy parameters.
Table 9 Parameters for creating a network policy Parameter
Description
Example
Policy Name
Customize the name for the network policy.
access-ingress3
Namespace
Select the namespace where the policy applies.
default
Selector
Enter a label selector for the target pod and click Add. If left empty, all pods in the namespace are selected. Click Reference Workload Label to use an existing workload's label.
Key: role
Value: db
Inbound Rule
Click
 to add an inbound rule.
Outbound Rule
Click
 to add an outbound rule.
Table 10 Parameters for adding an inbound rule Parameter
Description
Example
Protocol & Port
Select the protocol type and port. TCP and UDP are supported.
Protocol: TCP
Port: 6379
Source CIDR Block
For clusters v1.27.16-r10, v1.28.15-r0, v1.29.10-r0, v1.30.6-r0, or later versions with DataPlane V2 enabled, you can configure the source CIDR block.
The specified source CIDR block allows traffic from a destination CIDR block (multiple exception CIDR blocks can be specified). Separate the destination and exception CIDR blocks using a vertical bar (|). If there are multiple exception CIDR blocks, separate them using commas (,). For example, 172.17.0.0/16|172.17.1.0/24,172.17.2.0/24 allows traffic from 172.17.0.0/16 except 172.17.1.0/24 and 172.17.2.0/24.
N/A
Source Namespace
Select a namespace whose objects can be accessed. It defaults to the policy's namespace if unspecified.
default
Source Pod Label
Enter a label selector for the allowed source pods and click Add. If left empty, all pods in the source namespace are permitted.
Key: role
Value: frontend
Table 11 Parameters for adding an outbound rule Parameter
Description
Example
Protocol & Port
Select the protocol type and port. TCP and UDP are supported. If unspecified, all protocols and ports are permitted.
N/A
Destination CIDR Block
Allow requests to be routed to a specified CIDR block (and not to the exception CIDR blocks). Separate the destination and exception CIDR blocks using a vertical bar (|). If there are multiple exception CIDR blocks, separate them using commas (,). For example, 172.17.0.0/16|172.17.1.0/24,172.17.2.0/24 allows 172.17.0.0/16 except 172.17.1.0/24 and 172.17.2.0/24.
N/A
Destination Namespace
Select a namespace whose objects can be accessed. It defaults to the policy's namespace if unspecified.
default
Destination Pod Label
Label selector for the target pod permitted by this rule. If left empty, all pods in the destination namespace are allowed.
Key: role
Value: web
- Click OK.
Using a YAML File
- Create the access-egress2.yaml file.vim access-egress2.yaml
File content:
apiVersion: networking.k8s.io/v1kind: NetworkPolicymetadata:name: access-egress2namespace: defaultspec:policyTypes:- Ingress- EgresspodSelector: # This rule applies only to pods labeled role=db .matchLabels:role: dbingress: # This is an ingress rule.- from:- podSelector: # Allow access only from pods labeled role=frontend .matchLabels:role: frontendports: # Only TCP can be used to access port 6379.- protocol: TCPport: 6379egress: # This is an egress rule.- to:- podSelector: # The rule takes effect for pods with the role=web label.matchLabels:role: web - Run the following command to create the network policy defined in the access-egress2.yaml file:kubectl apply -f access-egress2.yaml
Expected output:
networkpolicy.networking.k8s.io/access-egress2 created